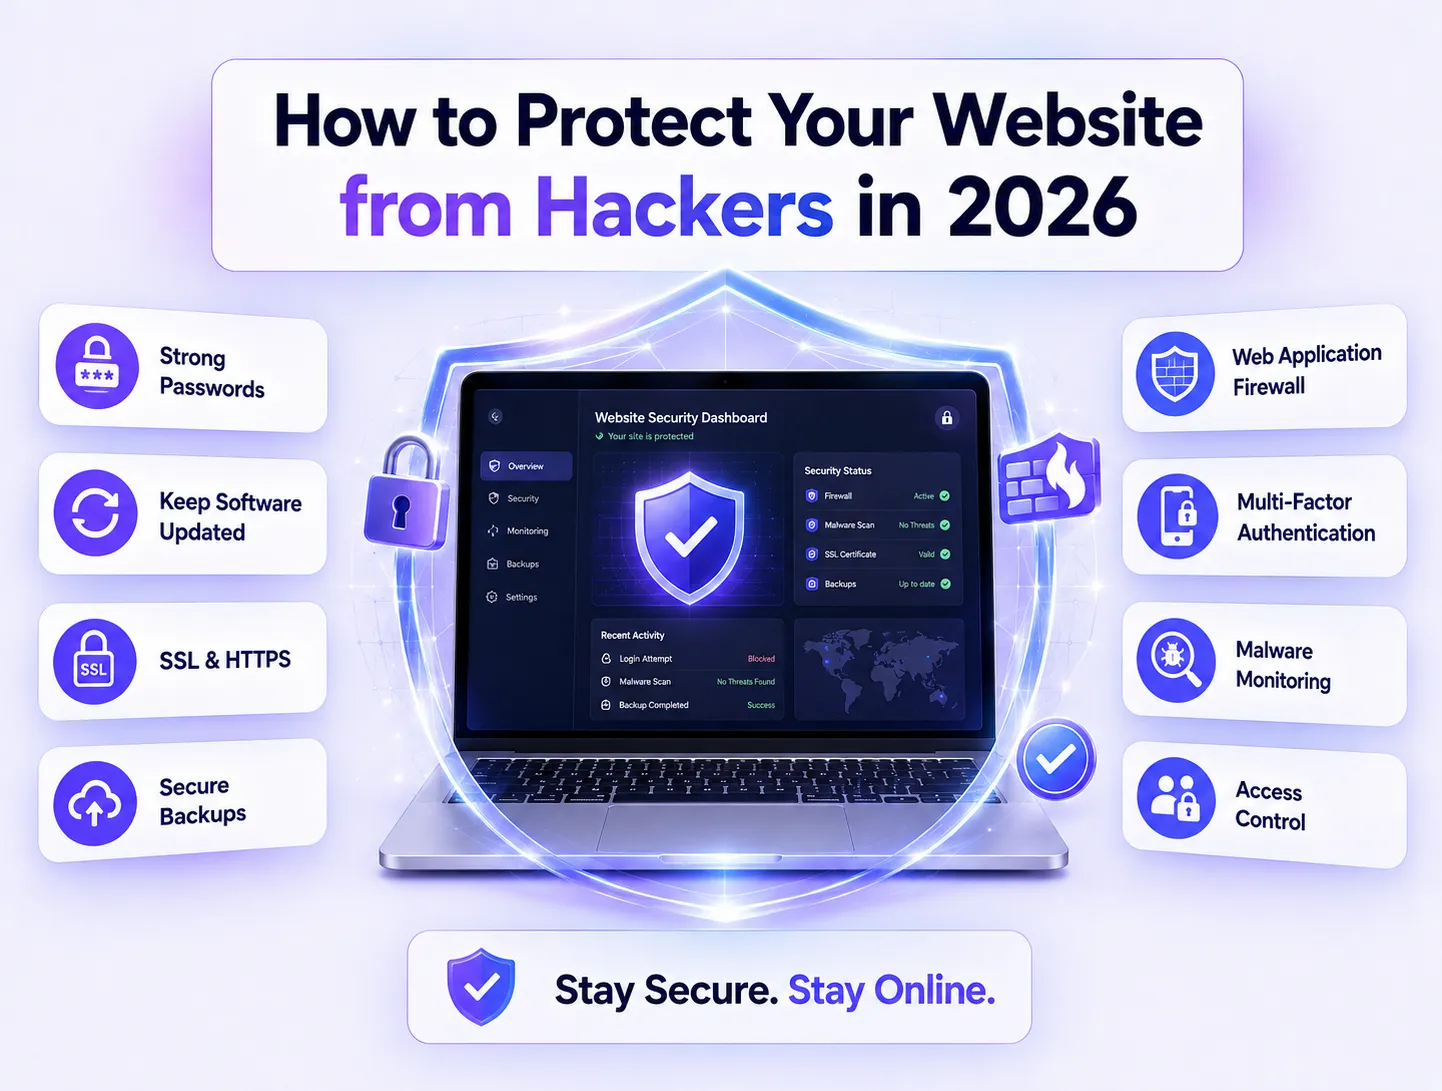
How to Protect Your Website from Hackers in 2026
Maintaining strong cyber defenses across your digital infrastructure is essential for safeguarding user data, protecting online sales channels, and sustaining search engine visibility. Modern cyber threats targeting commercial web applications range from automated credential stuffing to complex SQL injections and malicious script insertions. A single security breach can compromise confidential customer data, trigger search engine indexation warnings, and destroy brand trust overnight. Implementing comprehensive security practices during the initial engineering phase through professional custom website development ensures your business platform is fortified with clean code, encrypted data handling, and robust server-level access controls right from day one.
1. Enforcing Full HTTPS Encryption and TLS Certificates
Deploying Secure Sockets Layer encryption across your entire domain creates an encrypted communication tunnel between visitor web browsers and your hosting server. Transport Layer Security prevents malicious third parties from intercepting sensitive information like user passwords, personal contact details, or credit card transactions. Web browsers explicitly flag websites lacking valid TLS certificates as non-secure, scaring away prospective customers and causing conversion rates to collapse. Installing valid security certificates and enforcing HTTP-to-HTTPS redirects builds immediate consumer trust while meeting baseline search engine indexation requirements.
2. Hardening Content Management Systems and Updating Core Code
Outdated software frameworks, unpatched core files, and abandoned third-party plugins represent the primary entry points for automated hacker exploits. Cybercriminals deploy automated botnets to scan the web for known vulnerabilities in popular platforms like WordPress or Shopify. Securing your content management system requires removing unused plugins, enforcing routine software update schedules, and changing default database table prefixes. Partnering with engineering specialists who excel at WordPress development ensures your custom themes and plugin stacks receive regular security patches without breaking front-end user experience.
3. Restricting Admin Privileges and Enforcing Multi-Factor Authentication
Unrestricted administrative privileges and weak password policies leave corporate web platforms vulnerable to unauthorized account takeover attacks. Applying the principle of least privilege ensures that content creators, store managers, and external contractors only receive the minimum permissions necessary to perform their roles. Enforcing mandatory two-factor authentication across all staff logins creates a vital defense layer that stops brute-force attacks even if administrative credentials become compromised. Furthermore, limiting login attempt thresholds prevents malicious scripts from guessing passwords through automated dictionary attempts.
4. Deploying Web Application Firewalls and Malware Scanners
Integrating an intelligent Web Application Firewall acts as a digital shield that inspects incoming HTTP traffic before it reaches your hosting server. A properly configured WAF automatically filters out malicious bot traffic, blocks Cross-Site Scripting attempts, and mitigates distributed denial-of-service floods. Combining firewall protection with automated malware scanning utilities ensures that suspicious file modifications or unauthorized backdoors get quarantined instantly. This continuous monitoring preserves site uptime, safeguards your database integrity, and protects your server performance.
5. Securing Ecommerce Stores and Online Payment Gateways
Ecommerce platforms handling customer transactions require specialized security protocols to maintain Payment Card Industry compliance and protect sensitive financial data. Ensuring secure checkout flows, isolated database environments, and validated payment gateway APIs protects buyers from malicious checkout scripts. Businesses expanding globally through specialized Shopify store setups must combine secure front-end designs with hardened administrative controls to ensure uninterrupted, safe transaction processing.
Essential Website Security Measures Comparison Matrix
| Security Layer | Primary Threat Prevented | Business Impact of Failure | Recommended Protection Action |
|---|---|---|---|
| HTTPS / TLS Encryption | Data interception & man-in-the-middle attacks | Browser security warnings & drop in conversions | Enforce SSL across all pages and API endpoints |
| Web Application Firewall | DDoS attacks, XSS & SQL injections | Server downtime & corrupted database files | Deploy cloud WAF with real-time bot filtering |
| Multi-Factor Authentication | Brute-force login attempts & stolen passwords | Unauthorized site modification & admin lockout | Enforce 2FA for all administrative user accounts |
| Automated Remote Backups | Ransomware, server failure & malicious file edits | Permanent loss of customer data & website assets | Schedule daily off-site encrypted backups |
| Secure UI/UX Frontend | Phishing confusion & malicious pop-up redirects | Damaged user trust & lost checkout completions | Implement secure custom UI/UX design layouts |
6. Aligning Security Architecture with Intuitive UI/UX Design
Implementing rigorous back-end security measures should never compromise overall site navigation, visual elegance, or consumer usability. Intrusive CAPTCHA challenges or complex verification barriers can irritate visitors and lead to abandoned user journeys. Working with creative specialists focused on modern UI/UX design ensures that security prompts, account authentication flows, and payment verification screens remain intuitive, visually engaging, and completely frictionless for mobile and desktop users.
7. Automating Encrypted Off-Site Backups and Disaster Recovery
Even the most robust cyber defenses require a reliable disaster recovery strategy to ensure business continuity in the event of hardware failures or sophisticated breaches. Maintaining automated, encrypted daily backups stored on isolated cloud servers allows webmasters to restore clean site versions within minutes. Testing recovery workflows regularly guarantees that database tables, source code repositories, and user directories remain completely recoverable without experiencing catastrophic data loss.
8. Safeguard Multi-Channel Marketplace Seller Accounts
For brands operating beyond independent web properties, protecting external sales channels is equally critical to sustaining corporate revenue streams. Unauthorized access to enterprise merchant dashboards can lead to frozen funds, inventory tampering, or suspended store listings. Leveraging dedicated management for an Amazon Seller Central account ensures strict user permissions, secure API integrations, and two-step verification safeguards protect your global brand assets across competitive digital marketplaces.
9. Conducting Continuous Penetration Testing and Vulnerability Audits
Cyber security is an ongoing operational commitment rather than a static setup task. As new attack vectors emerge, conducting routine security audits, static code analysis, and penetration tests isolates potential system weaknesses before malicious actors exploit them. Inspecting error logs, auditing active administrative accounts, and reviewing server access patterns allows development teams to patch vulnerabilities proactive, maintaining long-term platform resilience.
10. Sustainable Web Security Execution for Enterprise Growth
Achieving absolute peace of mind requires aligning robust web security engineering with high-performance web development and creative digital strategy. Protecting your digital assets ensures uninterrupted sales operations, protected user relationships, and resilient organic search rankings. Collaborating with full-service agency experts at Webnestech equips your business with secure custom web applications, optimized ecommerce platforms, and end-to-end digital marketing solutions designed for long-term commercial dominance.
Frequently Asked Questions
Essential diagnostic questions regarding website security, malware protection, and securing online business platforms.
Hackers typically exploit outdated plugins, unpatched CMS software, weak admin passwords, unencrypted data connections, or malicious file upload forms.
No, an SSL certificate encrypts data in transit between the server and user browser, but you still need firewalls, software updates, and strong access controls to prevent hacking.
Isolate your site, change all admin credentials, scan for malicious code backdoors, restore a clean off-site backup, and update all software packages.
High-traffic websites and ecommerce stores should run automated daily off-site backups, while standard business sites should backup at least weekly.
Yes, Google flags hacked websites with security warnings, de-indexes compromised pages, and suppresses rankings to protect web searchers from malware.
Need expert help securing your website platform?
Our custom development and security team is here to audit and fortify your digital infrastructure.